
CVE-2026-99999, also known as PwnEscape, is a Linux kernel vulnerability that can break isolation between a virtual machine and its host. If you run a VPS, the urgent question for your provider is whether the host is running a fixed kernel. Updating Linux inside your VPS does not update that physical server.
Sources checked: October 17, 2026. The CVE record was published on October 15. This guide separates technical capabilities, documented demonstrations and operational recommendations. It is not an exploitation test or a server audit. CVE-2026-99999 in NVD.
What is PwnEscape, and why does it matter for a VPS?
The flaw is in the Linux kernel's IPv4 processing: some checksum metadata—the information used to check network packets—is not properly validated. This can corrupt data during packet handling. It is not a website or password vulnerability: it affects a system layer that processes virtual-machine traffic. The fix adds a check before completing the checksum. Fix merged into the Linux kernel.
In a vulnerable configuration, someone controlling a virtual machine may attempt to reach its host. The defect is not in KVM itself, but in the Linux networking stack involved in that environment. Researcher Paulos Yibelo documented a memory leak and a subsequent escalation to a host escape on his own systems. PwnEscape technical write-up reproduced on oss-security.
For background, our guide to what a VPS is and how it works explains the difference between your virtual server and the shared physical machine.
What could an attacker do?
Red Hat describes three possible outcomes: memory disclosure, a system crash and code execution on the host. Its CVSS assessment is 8.8, compared with 9.3 in the CVE record; required privileges are one difference. Both use a local attack vector. This does not mean the attacker must physically enter a data center. Red Hat's assessment and impact description.
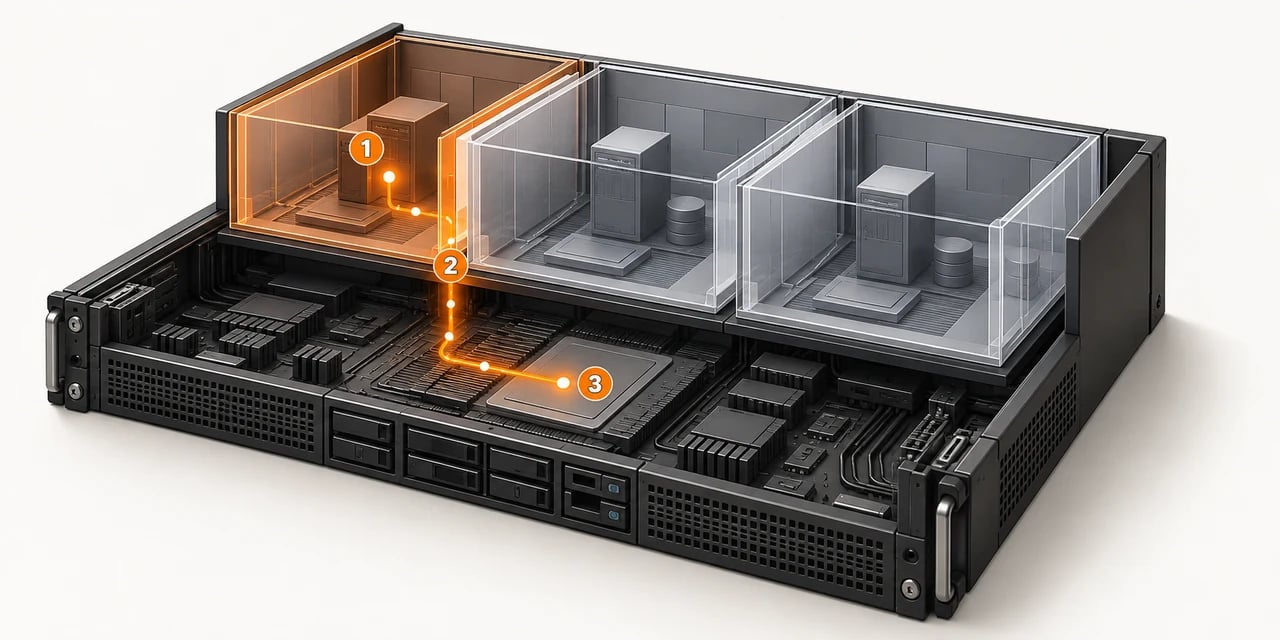
AI-generated illustration, not an incident screenshot. 1: an attacker-controlled virtual machine. 2: the vulnerable isolation boundary. 3: the Linux host. This shows a possible scenario, not evidence that every hosted VM was compromised.
Hypothetical example: if a host ran 20 VPS instances and an attack stopped that host, services on those 20 instances could be interrupted. This is not a PwnEscape victim count. It explains why a shared-layer failure may also affect customers who never ran malicious software.
Real-world scope: what has and has not been demonstrated
Vercel confirmed host-memory disclosure in production sandboxes. Host crashes and administrator-level code execution were demonstrated on the researcher's own KVM and Firecracker machines matching its configuration. Vercel said no reports showed access to customer files, secrets or application data. That does not mean every memory leak is harmless. Vercel's October 14 report.
We do not have a verifiable global count of compromised servers. The sources reviewed do not justify treating Linux installations, bug-bounty submissions or the age of vulnerable code as actual victims. They also do not establish that every provider is exploitable in the same way.
| Your situation | Meaning and next check |
|---|---|
| VPS on a vulnerable Linux host | Provider priority: patch the host kernel and verify that the fix is active. |
| Dedicated Linux server with untrusted users or workloads | Do not dismiss the issue simply because you do not sell VPS instances. Check the advisory for your distribution and configuration. |
| Windows VM hosted on Linux | This is not a Windows kernel CVE. A host crash or compromise could still affect service: the host OS matters too. |
| WordPress, a database or a game server | These are not the defective component in this CVE. Infrastructure failure can affect them; updating only the application does not patch the host. |
| Host with a valid fix already active | This addresses the specific vulnerability. It does not establish the absence of earlier incidents or remove other security risks. |
This table translates the kernel flaw into hosting decisions. Application consequences are impact scenarios, not confirmed incidents involving those products.
Fixed kernels for Debian 12 and Debian 13
Debian's official tracker identifies these fixed versions of the linux source package. They are not strings that must match uname -r literally.
| Distribution | Fixed version | Advisory |
|---|---|---|
| Debian 12, Bookworm | 6.1.190-1 | DLA-4841-1 |
| Debian 13, Trixie | 6.12.113-1 | DSA-6568-1 |
Checked October 17: Debian's CVE-2026-99999 status. For vendor kernels, backports or custom images, request the matching advisory. A different version number alone proves neither vulnerability nor protection.
Other distributions: on October 16, AlmaLinux announced fixed kernels in its testing repository for branches 8, 9 and 10. Testing availability is not the same as a stable production update; check for subsequent changes. For Ubuntu or RHEL, consult the specific release and kernel variant in its advisory. AlmaLinux status · Ubuntu status.
Quick check: what you can verify inside your VPS
These read-only commands do not modify your system. On Linux with systemd, they identify the distribution, running kernel and detected virtualization. They are not a PwnEscape or infection detector.
Choose a VPS with up-to-date infrastructure
TERAMONT has updated its Debian 12 and 13 nodes to kernels that fix this CVE. Explore our plans and choose the resources for your project.
cat /etc/os-release
uname -r
systemd-detect-virt
/etc/os-releaseidentifies the system where the command runs.uname -rshows that system's active kernel. In a VM with its own kernel, it does not reveal the host kernel.systemd-detect-virtmay reportkvm, another environment ornone. A missing command or undetected virtualization does not certify safety.
Keep this information for support. Assessing the host requires the provider's inventory and patch advisory. Do not run escape proofs of concept on a production VPS: they can interrupt other customers' services and are unnecessary for patch verification.
A message you can send your provider
Hello. Please confirm the CVE-2026-99999 (PwnEscape) status of my VPS host:
1. Which package or security advisory fixes the host kernel?
2. Is the fix already active, or is a reboot/patch activation pending?
3. When was it applied, and are migration destination nodes covered too?
4. Is any action required inside my VPS?
Thank you. I do not need information about other customers.
How to patch it: installed is not the same as active
If you administer the host, we recommend this workflow. If you administer only a VPS, coordinate the host-side work with your provider.
- Identify the kernel and applicable advisory. Check the distribution, variant and package. Use official repositories or your platform's supported update.
- Prepare maintenance and recovery. Verify recoverable backups and console access. Rebooting a host may interrupt its VPS instances; any migration must land on a patched node too.
- Install the fixed update. Review the package manager's proposed changes before accepting them. Do not install a testing kernel or release candidate merely because its number looks newer.
- Activate the fix. This normally means booting the new kernel. Livepatch counts only when its provider confirms coverage of this CVE and successful application.
- Verify the result. Check the kernel actually running, its relationship to the advisory and every node's status. Keep the guest system updated separately.
A firewall, a new SSH password or rebooting only the VM does not replace the host patch. In the advisory reviewed, Red Hat does not list a general mitigation meeting its deployment and stability criteria.
How can you tell whether an attack already happened?
A vulnerable version does not mean a server was compromised; a patched one does not prove nothing happened earlier. As an operational response, preserve logs and ask the provider to investigate the host if you observe unexplained restarts, integrity alerts or unusual activity. These signs are not specific to PwnEscape. If compromise is confirmed, isolation, rebuilding from a trusted baseline and credential rotation belong in an incident-response plan—not a supposedly guaranteed cleanup.
TERAMONT's status and your next step
TERAMONT has updated its Debian 12 and Debian 13 nodes to kernel versions that fix CVE-2026-99999, according to confirmation received from its management on October 17, 2026. This statement describes the update reported by TERAMONT. We are not presenting this article as an independent audit or a zero-risk guarantee.
If you are choosing hosting, explore TERAMONT VPS Hosting plans. For this incident, a useful provider-selection criterion is specific: confirmation of the host patch, its activation and node coverage. Security does not end with the purchase; applications and credentials inside your VPS still need maintenance.